The recent PHP vulnerability has prompted questions about potential risks to software systems and the steps organisations should take to protect their environments.
At Pro2col, we understand how important it is to stay informed. We’re committed to helping our clients access clear, practical advice and the latest information to help ensure their services remain unaffected.
Our technical team has conducted an audit of all systems and third-party tools used within Pro2col to establish no risks posed by the PHP vulnerability. We continue to monitor the situation and review relevant information from our software partners to ensure this remains the case.
You can see all of the current responses and fixes from our vendor partners listed below.
Globalscape EFT
Fortra have confirmed that Globalscape EFT is not affected. No exposure was identified in the reviewed EFT core code, or available library and dependency definitions. HTTP services reviewed and web APIs use native C++ implementations. Fortra have found no PHP runtime dependency or PHP execution integration in these components. Based on these findings, EFT is therefore not affected by these vulnerabilities, and no remediation is required for those components. This assessment applies specifically to the reviewed EFT codebase and its product dependencies. It does not assess other applications, libraries, scripts, or services that the customer may independently install or use outside EFT.
GoAnywhere MFT and FileCatalyst
Fortra has confirmed that GoAnywhere MFT and FileCatalyst is affected by these vulnerabilities. Neither product family uses PHP, and no patches, upgrades or configuration changes are required to address these CVEs.
GoAnywhere MFTaaS
Fortra have reported, these environments have been reviewed and are not affected by the PHP vulnerabilities. No customer action is required.
MOVEit Transfer, MOVEit Automation, MOVEit Gateway, Automate
Progress Software has confirmed that MOVEit Transfer, MOVEit Automation, MOVEit Gateway and Automate MFT are not affected by the PHP vulnerability, as none of these products use PHP. No action or remediation is required in relation to this vulnerability. View Progress’ full statement on the PHP vulnerabilities here.
Files.com
Files.com has confirmed that it is not affected by the PHP vulnerabilities (CVE-2026-109618 and CVE-2026-109619), as PHP is not used anywhere within the Files.com product.
Coviant Diplomat
Coviant has confirmed that Diplomat MFT does not use PHP within its platform and is not affected by the recent PHP vulnerabilities.
JAMS
JAMS Scheduler, JAMS Incident Management, and Skybot Scheduler are not affected by these vulnerabilities. Their R&D team reviewed all three products. None of them includes, bundles, or depends on PHP. This covers:
- JAMS Scheduler, including the Scheduler service, Agents, Desktop Client, Web Client, and REST API
- JAMS Incident Management
- Skybot Scheduler
If you run PHP scripts through JAMS Scheduler jobs, those jobs use your own PHP installation, not one supplied by JAMS. Therefore, patching of this installation should take place as you normally would.
View JAMS’ full statement on the PHP vulnerabilities here.
WS_FTP
Progress Software have confirmed that WS_FTP Server and WS_FTP Professional are not affected by the PHP2Shell vulnerability, as neither product uses PHP. No action or remediation is required in relation to these vulnerabilities. View Progress’ full statement here.
CloudMFT
Pro2col can confirm that any identified vulnerability has now been fully remediated on the affected system(s) hosting CloudMFT services. Post-remediation validation has been completed, and all affected services continue to operate normally. At this time, there is no further action required.
CData Arc
CData has confirmed that Arc does not use PHP in its product or components and is therefore not affected by the vulnerability. No PHP updates or additional mitigations are required.
Cleo VLTrader, Harmony
Cleo has confirmed that the products listed below are not affected by these vulnerabilities:
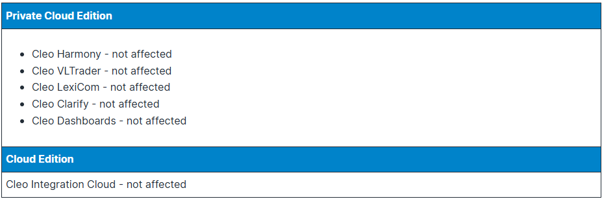
Cleo WebEDI, part of its Compliance Edition, has been patched to protect against these vulnerabilities.
View Cleo's full statement here.
ICAP
Fortra have reported, these vulnerabilities do not affect any of the secure gateway products. Their statement can be found here.
Maytech Quatrix
Maytech has advised that they have patched PHP versions to include the fixes as per the official advisories.
Accolm BAM
There are currently no known security advisories indicating that Accolm BAM is affected by the PHP vulnerability.
Note: Customers who independently use PHP in other applications or components within their environments should assess those separately and follow the applicable vendor’s security guidance.
At this time, no affected systems have been identified, and no immediate action is required. We will continue to monitor the situation and update this article as further information becomes available. If you have any questions or concerns about how these vulnerabilities may affect your file transfer environment, please get in touch with our team.